Web Sec
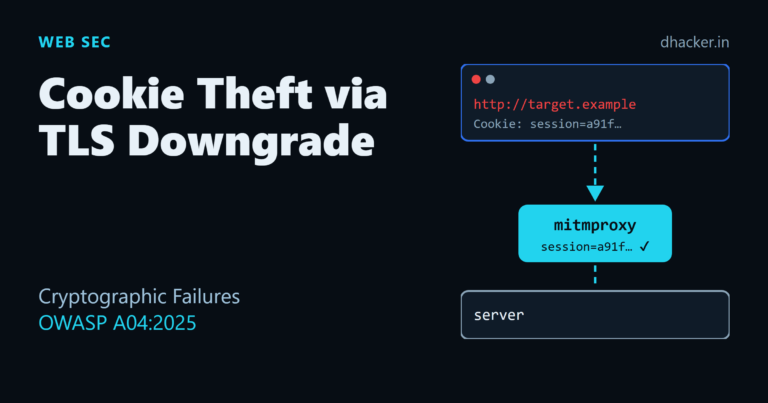
Cookie Theft via TLS Downgrade: Exploiting and Fixing Cryptographic Failures (OWASP A04:2025)
Use mitmproxy to steal a session cookie sent over plaintext HTTP, then fix it with HTTPS, Secure/HttpOnly/SameSite cookie flags, and…
Use mitmproxy to steal a session cookie sent over plaintext HTTP, then fix it with HTTPS, Secure/HttpOnly/SameSite cookie flags, and…
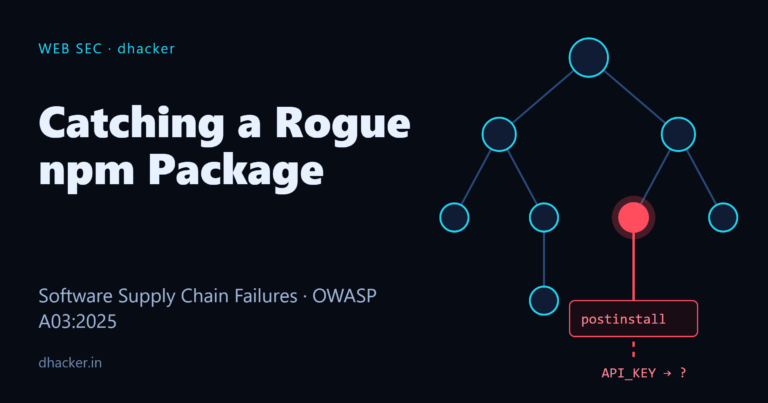
Build a Node.js project with a malicious postinstall script that exfiltrates a secret, then generate an SBOM, detect the rogue…
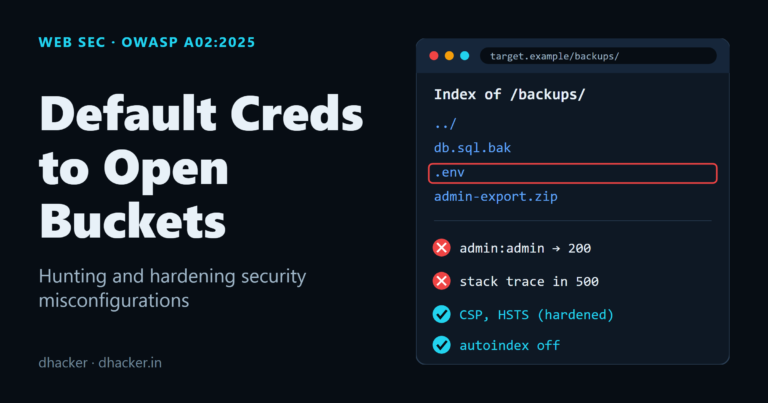
Scan a deliberately misconfigured Docker Compose stack with curl and nikto, then apply a hardened Nginx config and prove the…
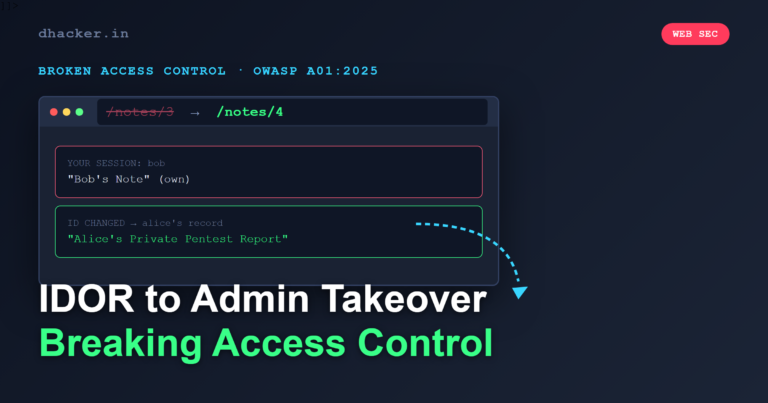
Walk through IDOR and forced-browsing exploits in a Flask notes app, then fix them with ownership checks and a role-required…
Most rate limiters fail under real traffic because they track requests per-minute instead of allowing bursts. Here’s a token bucket…