Web Sec
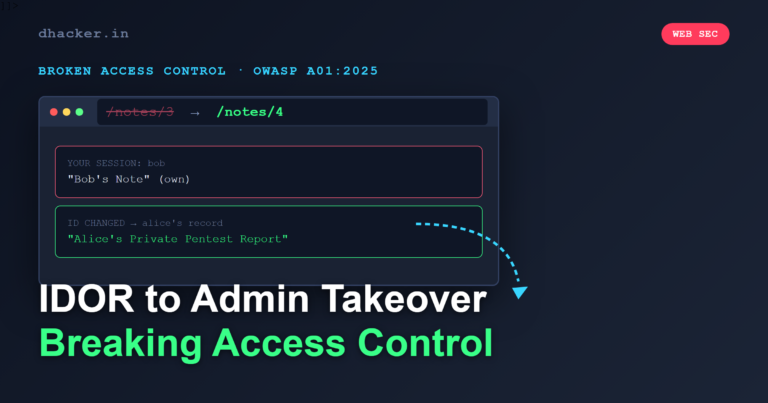
IDOR to Admin Takeover: Exploiting and Fixing Broken Access Control (OWASP A01:2025)
Walk through IDOR and forced-browsing exploits in a Flask notes app, then fix them with ownership checks and a role-required…
Walk through IDOR and forced-browsing exploits in a Flask notes app, then fix them with ownership checks and a role-required…
Most rate limiters fail under real traffic because they track requests per-minute instead of allowing bursts. Here’s a token bucket…