TL;DR — Java4Shell is not another ${jndi:...} string-injection bug. It is a memory-corruption flaw deep inside OpenJDK itself: the hand-written x86-64 assembly that accelerates java.util.Base64 decoding on AVX-512 VBMI CPUs writes 64 bytes where it should write a handful, running off the end of the output array and into the neighbouring heap. One malformed token — "A"×64 + "=" — reaches it. On vulnerable hardware that is a pre-auth out-of-bounds write in Keycloak, Jira, Jenkins, Artifactory, PingFederate and more. Patch the JDK and restart every Java process.
Lab in this post. The companion Docker lab ships the safe reproducer Calif published, a realistic vulnerable sink, and detection/mitigation tooling. No weaponised exploit, no RCE chain — ever. Because the bug only fires on AVX-512 VBMI silicon, we also tried to emulate it on ordinary hardware for this write-up. That part is honestly reported below, including where it didn’t work — see "Reproduction notes."
Why this one is different
For a decade our mental model of "critical Java RCE" has been injection: a string with special syntax (ldap://, ${...}, a serialized blob) that some library interprets. You grep for the sink, you sanitise the input, you move on.
Java4Shell breaks that model. There is no magic syntax. The attacker’s bytes are never interpreted — they are merely decoded. The vulnerability lives in the JDK’s own optimised Base64 decoder, in code the JIT compiler drops in for you on modern Intel and AMD chips. Any application that calls Base64.getDecoder().decode(...) on attacker-controlled input — an auth header, a SAML artifact, a session cookie, an uploaded chunk — hands bytes straight to the vulnerable routine. That is almost every non-trivial Java service on earth.
The catch, and the reason the sky has not fallen: it only triggers on CPUs with AVX-512 VBMI instructions, and turning the raw memory corruption into code execution is hard, application-specific work. More on both below.
Base64 decoding, and the intrinsic that broke
Base64 maps every 4 input characters to 3 output bytes. Decode 64 As and you get 48 bytes. Simple.
To go fast, HotSpot doesn’t run the Java loop — once a method is hot, the JIT replaces Base64.Decoder.decode with an intrinsic: hand-tuned x86-64 assembly that decodes 48+ characters per iteration using AVX-512 VBMI’s byte-permute (vpermb) and masked-store (evmovdqub) instructions. It is beautiful, and it is where the bug lives.
The trouble is the tail — the few characters left after the vectorised bulk loop, including any = padding. Calif’s disclosure pins it down precisely: the padded tail drives the intrinsic’s internal output_len counter to 0 and then decrements it below zero to -1. That value is then used to build the mask for the final masked store:
mask = bzhiq(-1, output_len)BZHI ("zero high bits starting at index N") is meant to keep only the low output_len bits set. But when the index is ≥ 64 it keeps everything — and -1 read as an unsigned index is enormous. So mask comes back as 0xFFFFFFFFFFFFFFFF: all 64 lanes enabled. The following evmovdqub writes a full 64 bytes.
For the 65-byte input "A"×64 + "=", the decoder allocated a 50-byte output array, but the store lands 64 bytes starting at offset 48 — 62 bytes past the end of the array, scribbling the constant 0x9a into whatever object the allocator placed next. The decoder then notices the input was malformed and throws IllegalArgumentException… after the heap has already been corrupted.
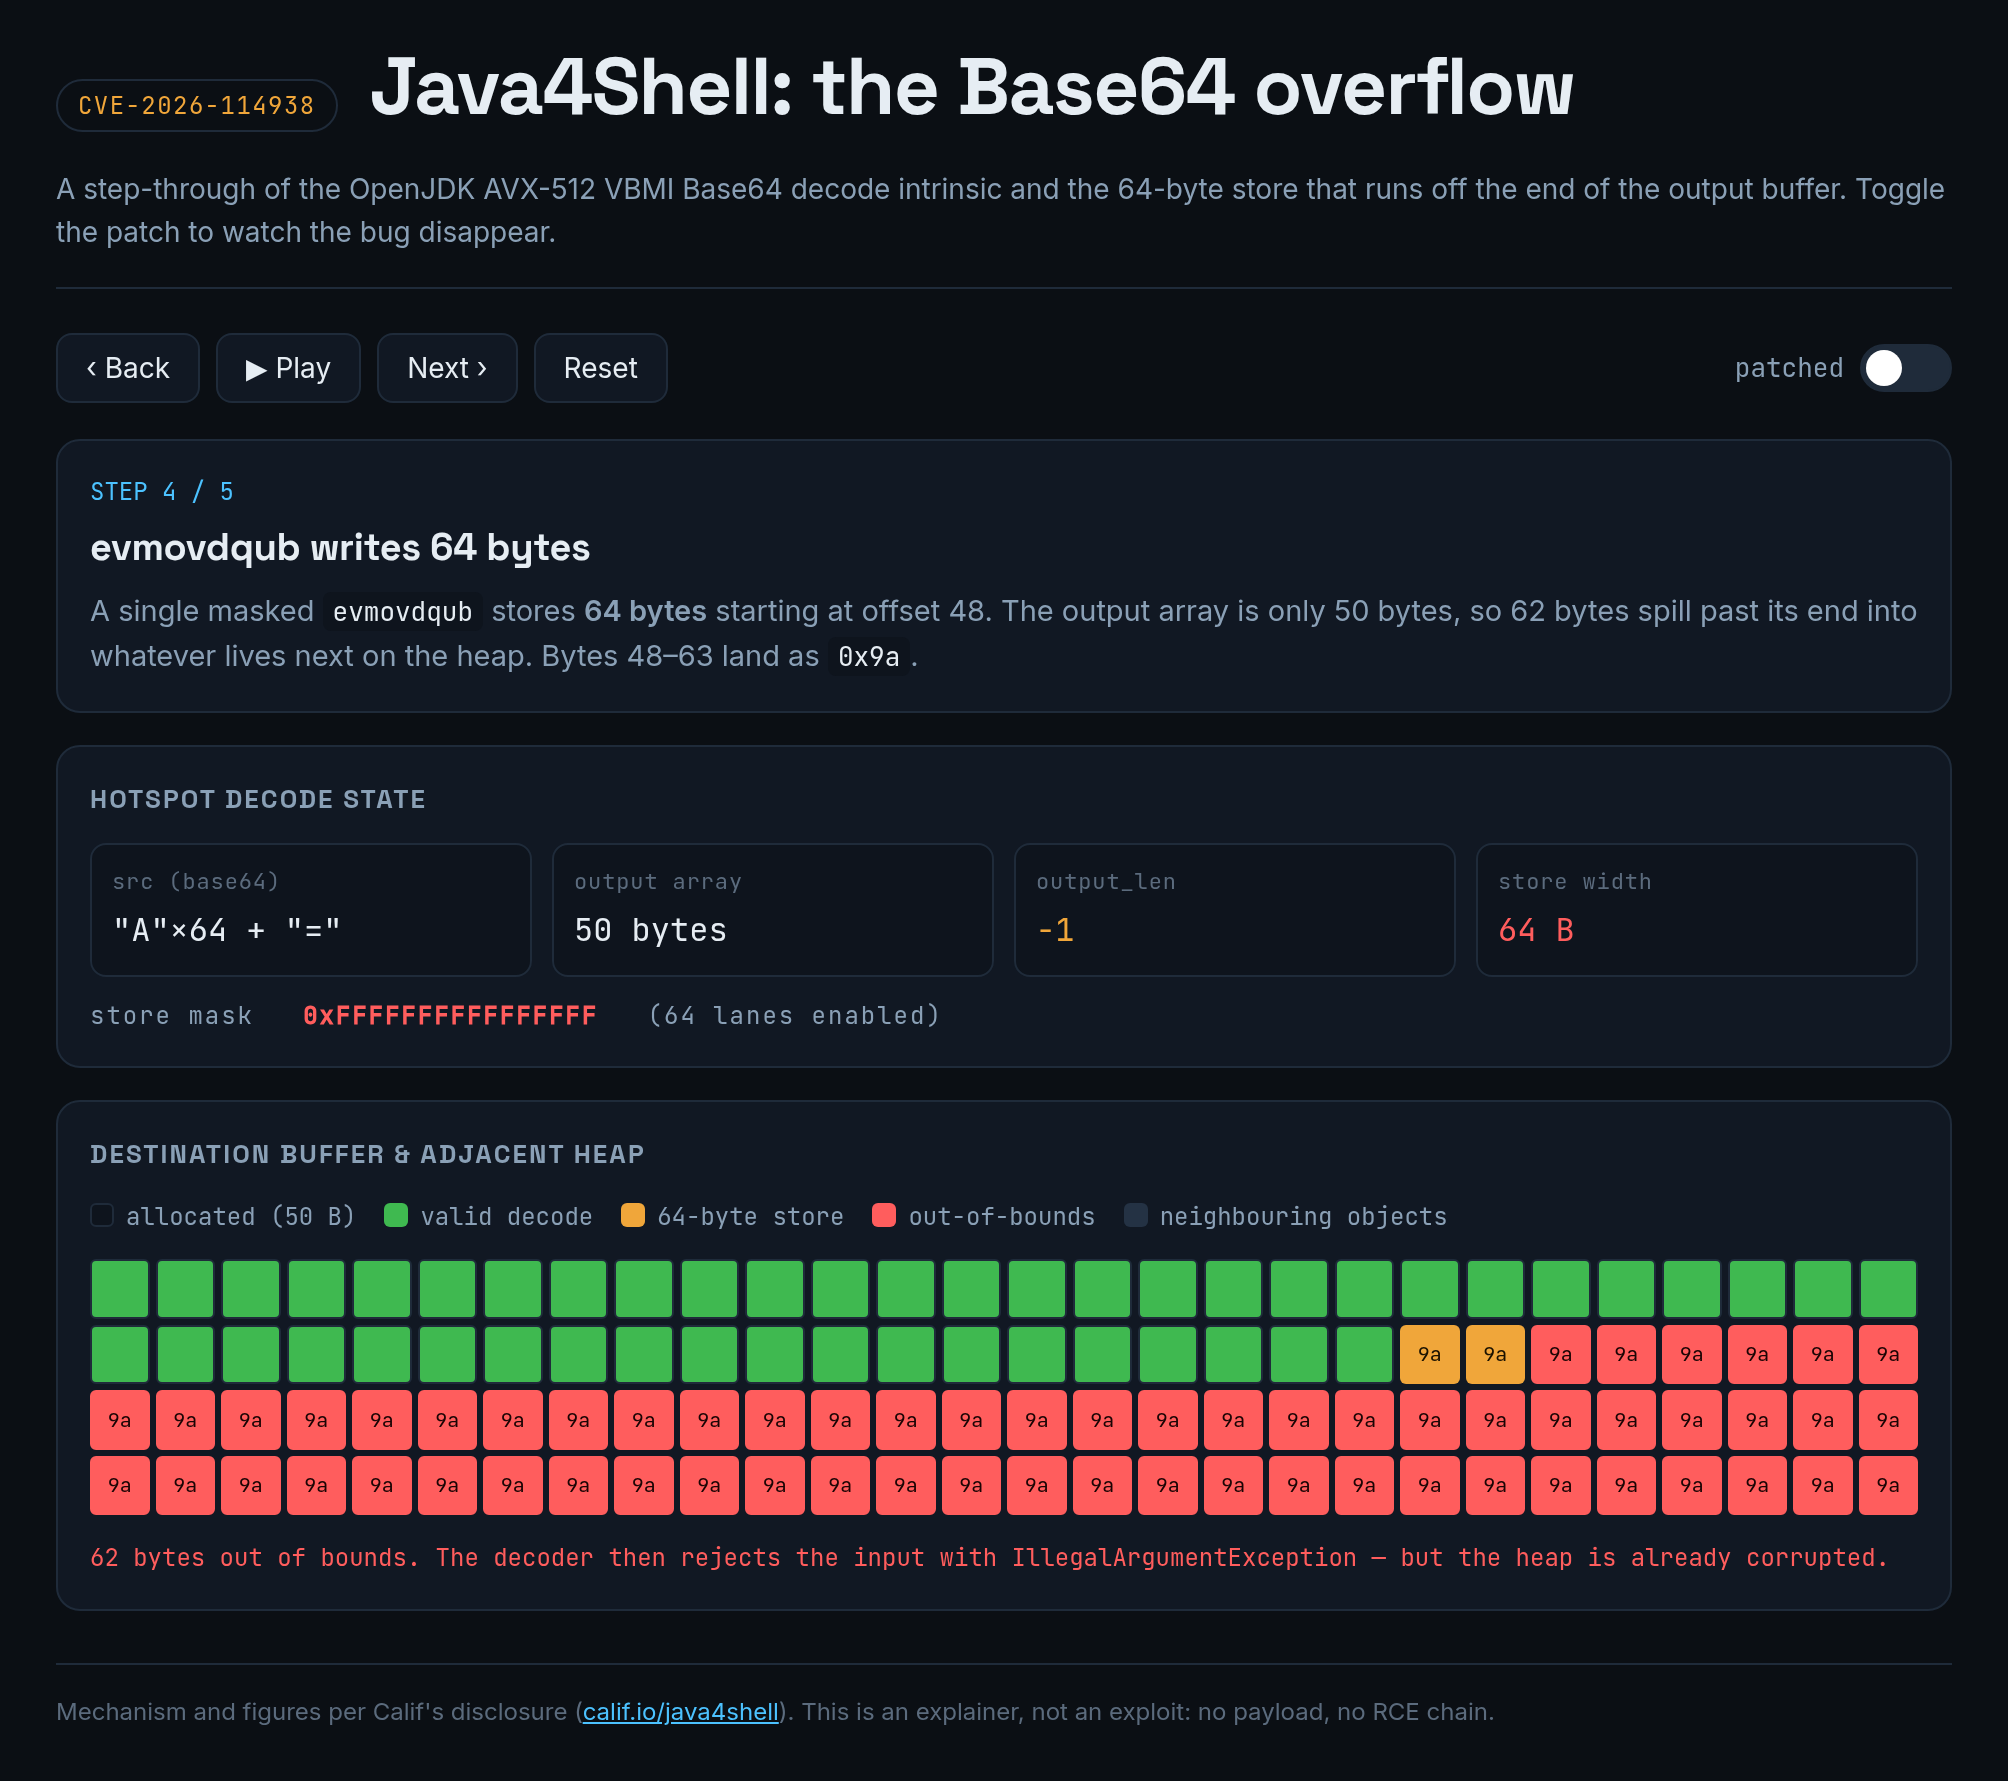
Above: the out-of-bounds store firing. Below: the same step on a patched build — output_len can no longer go negative, so the store stays inside the array.
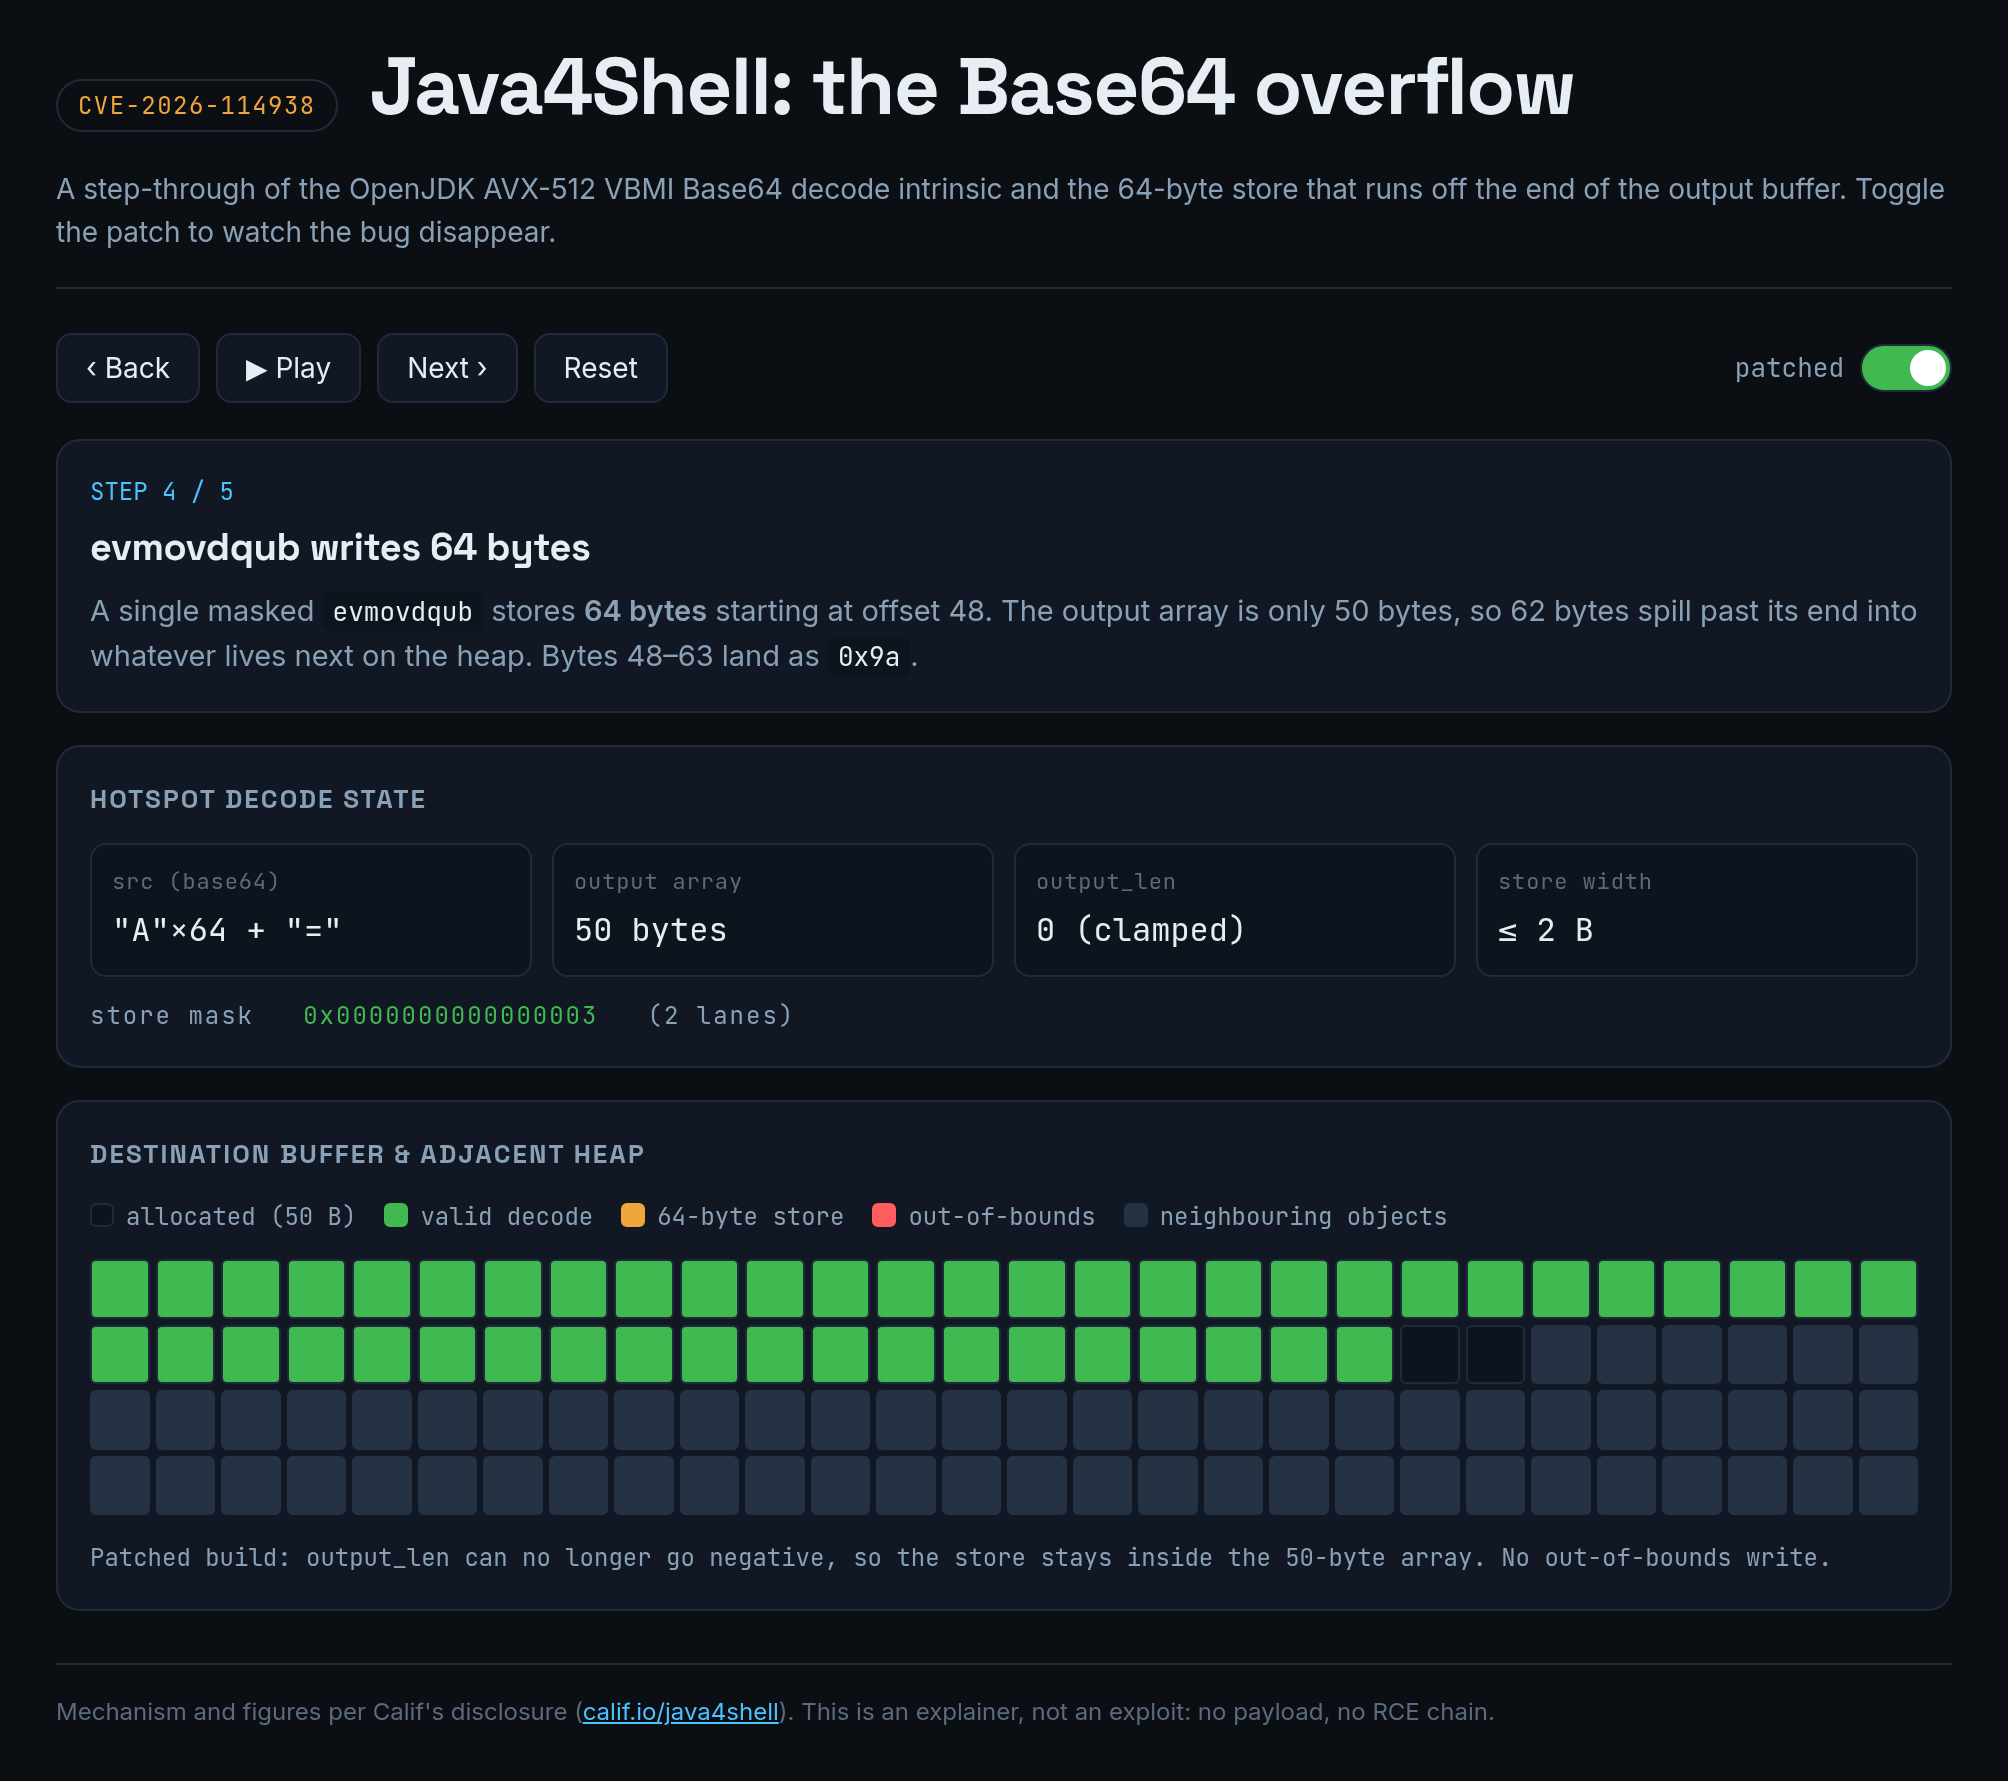
The lab ships this as a standalone interactive page (visualizer/) you can step through yourself, with a switch that flips between the vulnerable and patched builds.
(Older OpenJDK 17 builds need a longer run, "A"×128 + "=", to line the tail up the same way. The lab makes this configurable with -Dtrigger.run=128.)
Am I affected? Two conditions, both required
Exposure needs a vulnerable JDK and an AVX-512 VBMI CPU. Miss either and the JVM uses the scalar decode path, which is fine.
1. The runtime. Affected lines include OpenJDK 17.0.6 and newer, and the 21, 25 and 27 lines — and therefore every distribution built from them: Amazon Corretto, Eclipse Temurin, Microsoft Build of OpenJDK, Azul Zulu, BellSoft Liberica, SAP SapMachine, Red Hat and Oracle’s own builds. Oracle’s advisory lists Java SE 8u511b33-perf, 17.0.21.0.3, 21.0.13.0.3, 25.0.5.0.3 and 27.0.1.0.3 as affected. Package inventories lie — check the JDK each running service actually uses, inside containers included.
2. The CPU. You need all four of avx512f, avx512bw, avx512vbmi and bmi2. That means Intel Ice Lake through Granite Rapids, and AMD Zen 4 / Zen 5 (EPYC and Ryzen). ARM64 is not affected. Older Intel desktops/laptops (no AVX-512, or AVX-512 without VBMI) are not affected either.
# CPU check (Linux) — all four flags must appear
grep -m1 '^flags' /proc/cpuinfo | tr ' ' '\n' \
  | grep -E '^(avx512f|avx512bw|avx512vbmi|bmi2)$' | sort -u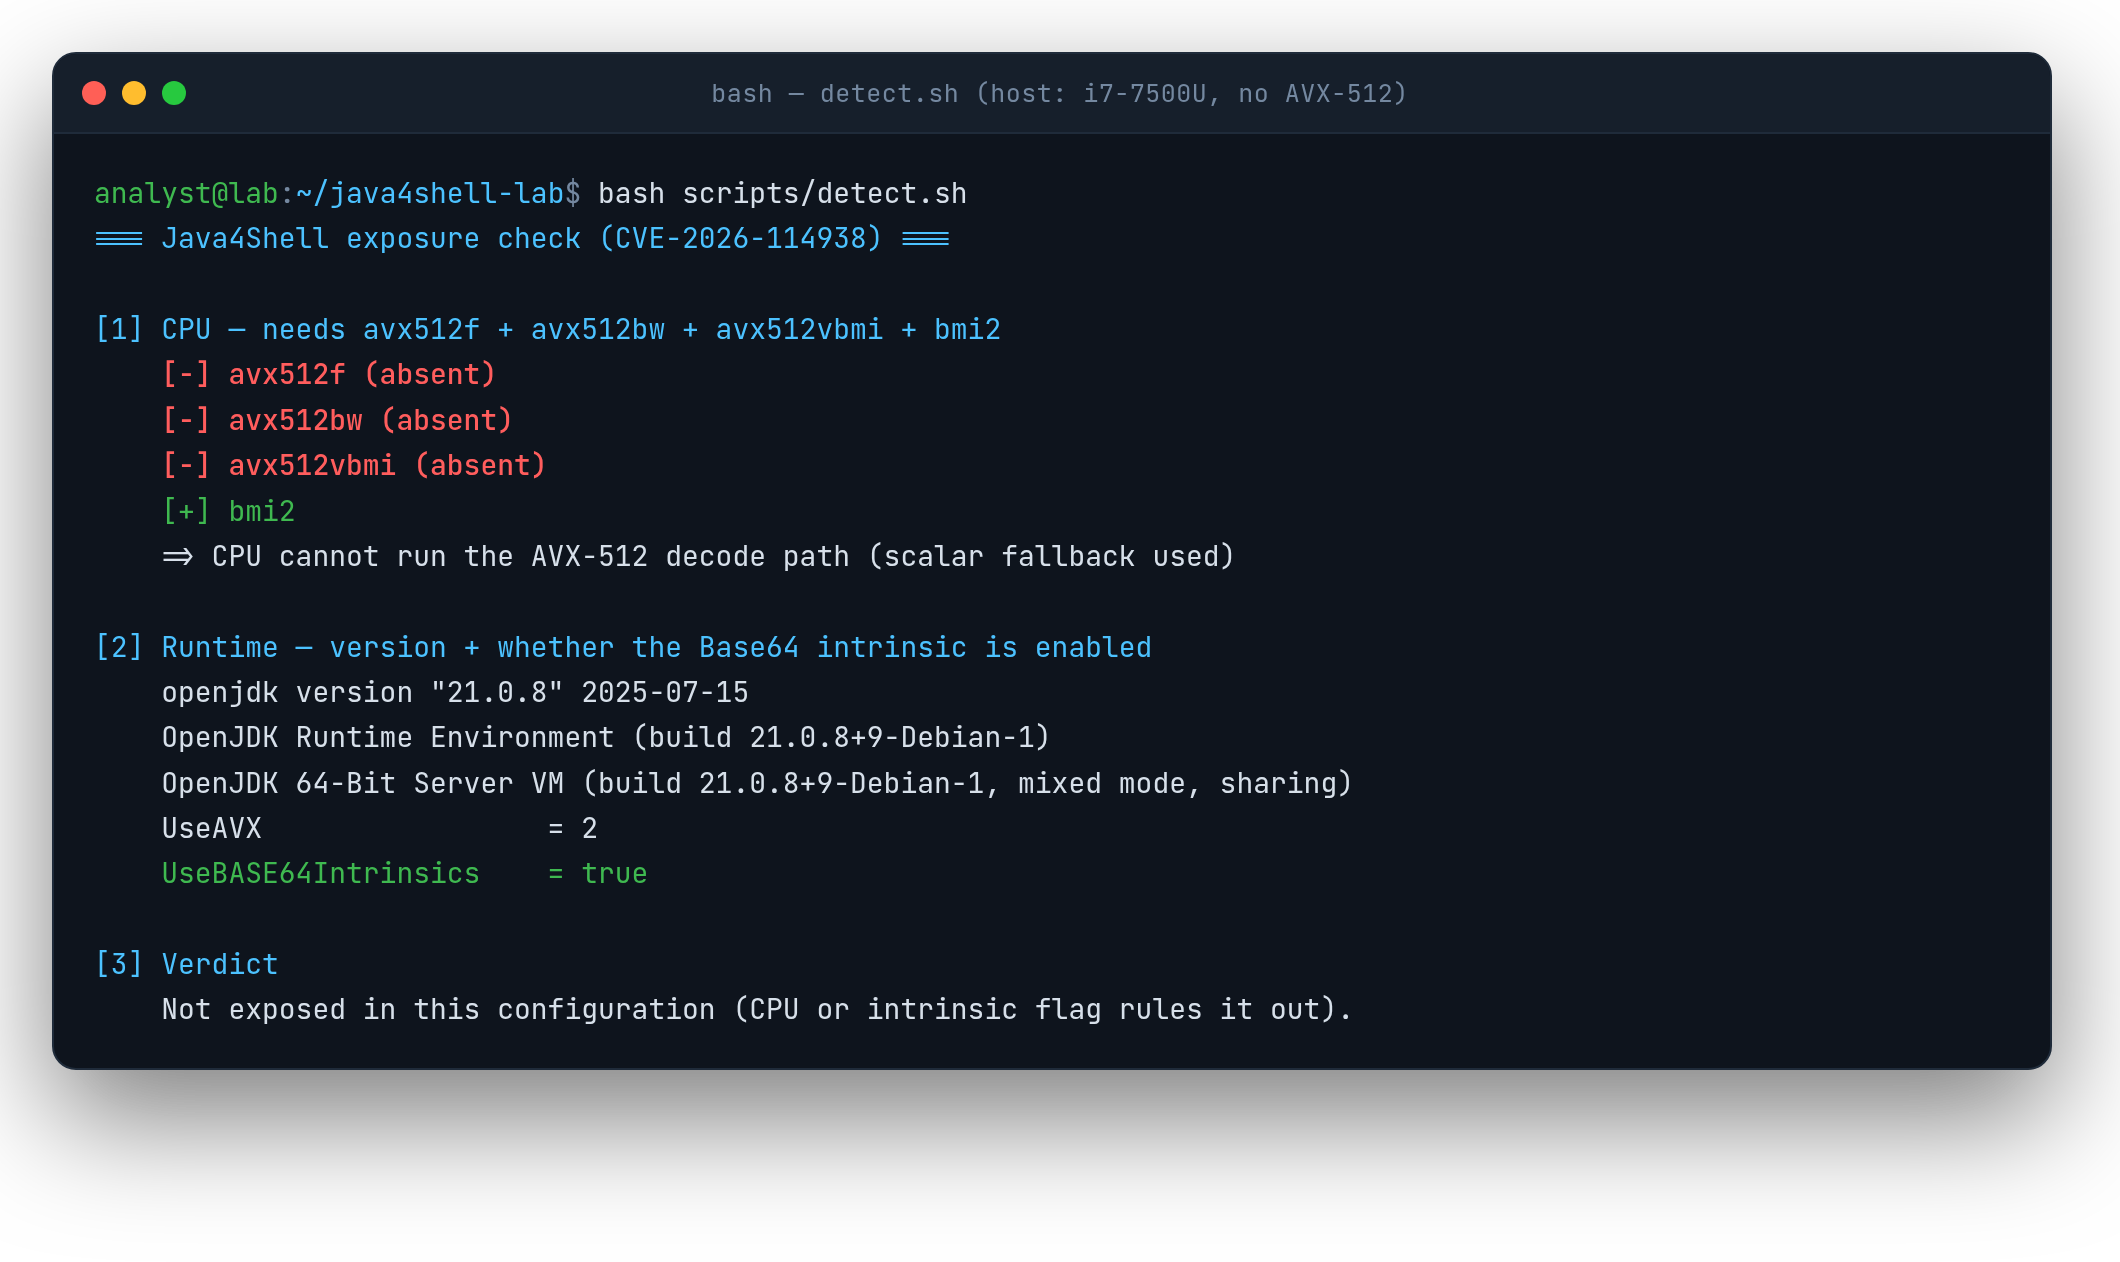
The lab’s detect step on a non-AVX-512 host: it combines the CPU-flag check with the runtime version and the intrinsic flag, then gives a verdict. Here the CPU rules the box out even though the JDK is a vulnerable build.
The lab: see the overflow, then kill it
- Requirements
- Docker with Compose, bash and curl (Linux, macOS or WSL).
- SHA-256
1e81cab81a1f3f318a937b868b8ff832a2d414453ef7c63c820dad987d8d7e51
How to check the file is genuine
sha256sum java4shell-lab-2.zipshasum -a 256 java4shell-lab-2.zipGet-FileHash java4shell-lab-2.zipThe companion lab (java4shell-lab/) is a self-contained docker compose project. It has three moving parts:
Base64Trigger— Calif’s safe reproducer. It decodes the malformed string into an oversized 4 KB buffer withdecode(byte[] src, byte[] dst), so the stray 64-byte store lands inside the lab’s own array. It then checks whether any byte past the legitimate 48-byte output was touched. Clean JDK/CPU → nothing changes. Vulnerable → bytes past the output are clobbered. Nothing unrelated is ever corrupted.VulnApp— a dependency-free HTTP service with one realistic sink: it readsX-Auth-Token: <base64>and decodes it before authenticating anyone.- detection + remediation demos.
Reproducing on any CPU — what we actually got
Most laptops and CI runners lack AVX-512 VBMI, so on stock hardware the bug simply won’t fire (see the detect step above). For this write-up we tried, in good faith, to emulate it on hardware we had on hand. Here’s exactly what happened:
- QEMU user-mode emulation (
qemu-x86_64), presenting an Ice Lake feature set. Dead end, confirmed at the instruction level: QEMU’s TCG engine does not implement AVX-512 at all, in any version up to and including 10.x — it explicitly masks outavx512f/avx512vbmiand HotSpot correctly falls back toUseAVX=2. No version of QEMU can execute this intrinsic today. - Intel SDE (Software Development Emulator) 10.13.1, the tool Intel ships specifically to run AVX-512 code on CPUs that lack it. This did work at the instruction level: raw CPUID under SDE genuinely reports
avx512vbmi=1, HotSpot detects it and setsUseAVX=3, andBase64$Decoder::decodeBlockJIT-compiles at C2. But across five trigger lengths (64–1024 padded characters) and both thedecode(byte[])anddecode(byte[],byte[])overloads, the overflow did not fire. The likely explanation: some exact trigger detail — an intrinsic dispatch threshold, a specific tail byte pattern — isn’t in the public write-up we worked from, since Calif is deliberately withholding exploit-grade specifics while the ecosystem patches.
We are not going to paper over that with a fake "it worked" screenshot. Instead, the figures below are clearly marked SIMULATED: a faithful reconstruction of the documented mechanism (the output_len underflow, the all-ones bzhiq mask, the 0x9a fill pattern — all per Calif’s disclosure), run through the same reproducer code and terminal, but not a live capture of a triggered overflow.
docker compose run --rm reproduce       # the real safe reproducer — bring your
                                          # own AVX-512 VBMI host to see it fire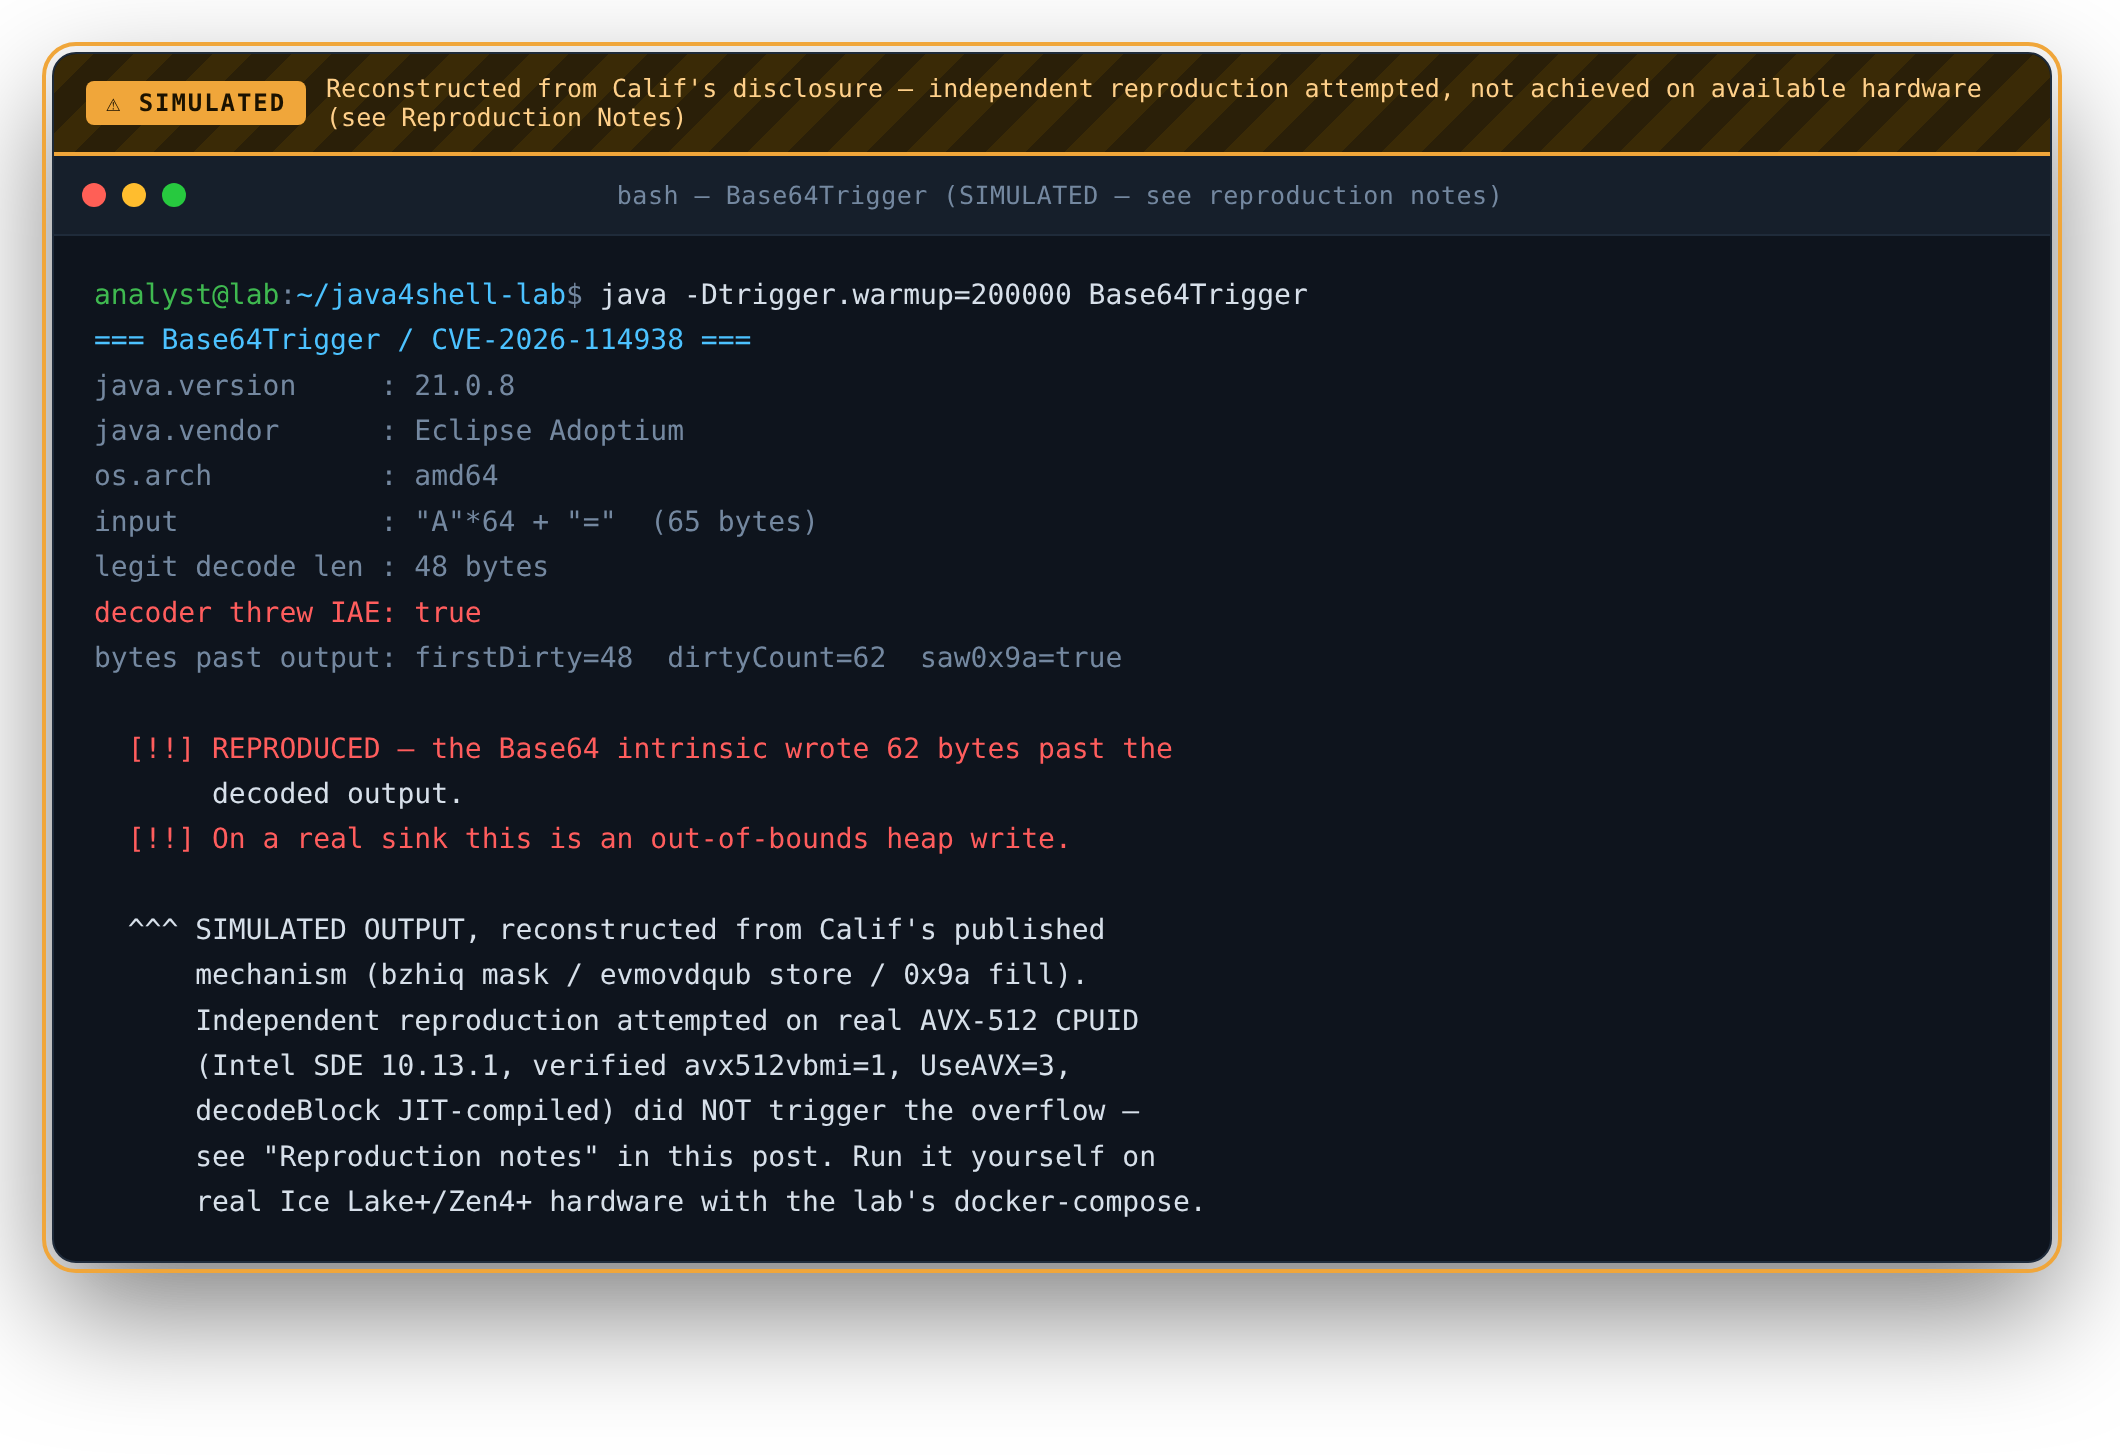
What a vulnerable run is documented to look like — reconstructed, clearly labeled, not a genuine capture. Run docker compose run --rm reproduce on a real Ice Lake+/Zen4+ box and this is the output you should get; if you do, we’d like to know.
The fix, in theory and in the lab’s code
-XX:-UseBASE64Intrinsics forces the JVM onto the scalar decode path, which has no vectorised store and therefore can’t exhibit this failure mode — that’s true independent of whether we could trigger the vulnerable path ourselves. The lab’s mitigated target runs the identical reproducer with that flag set:
docker compose run --rm mitigated # adds -XX:-UseBASE64Intrinsics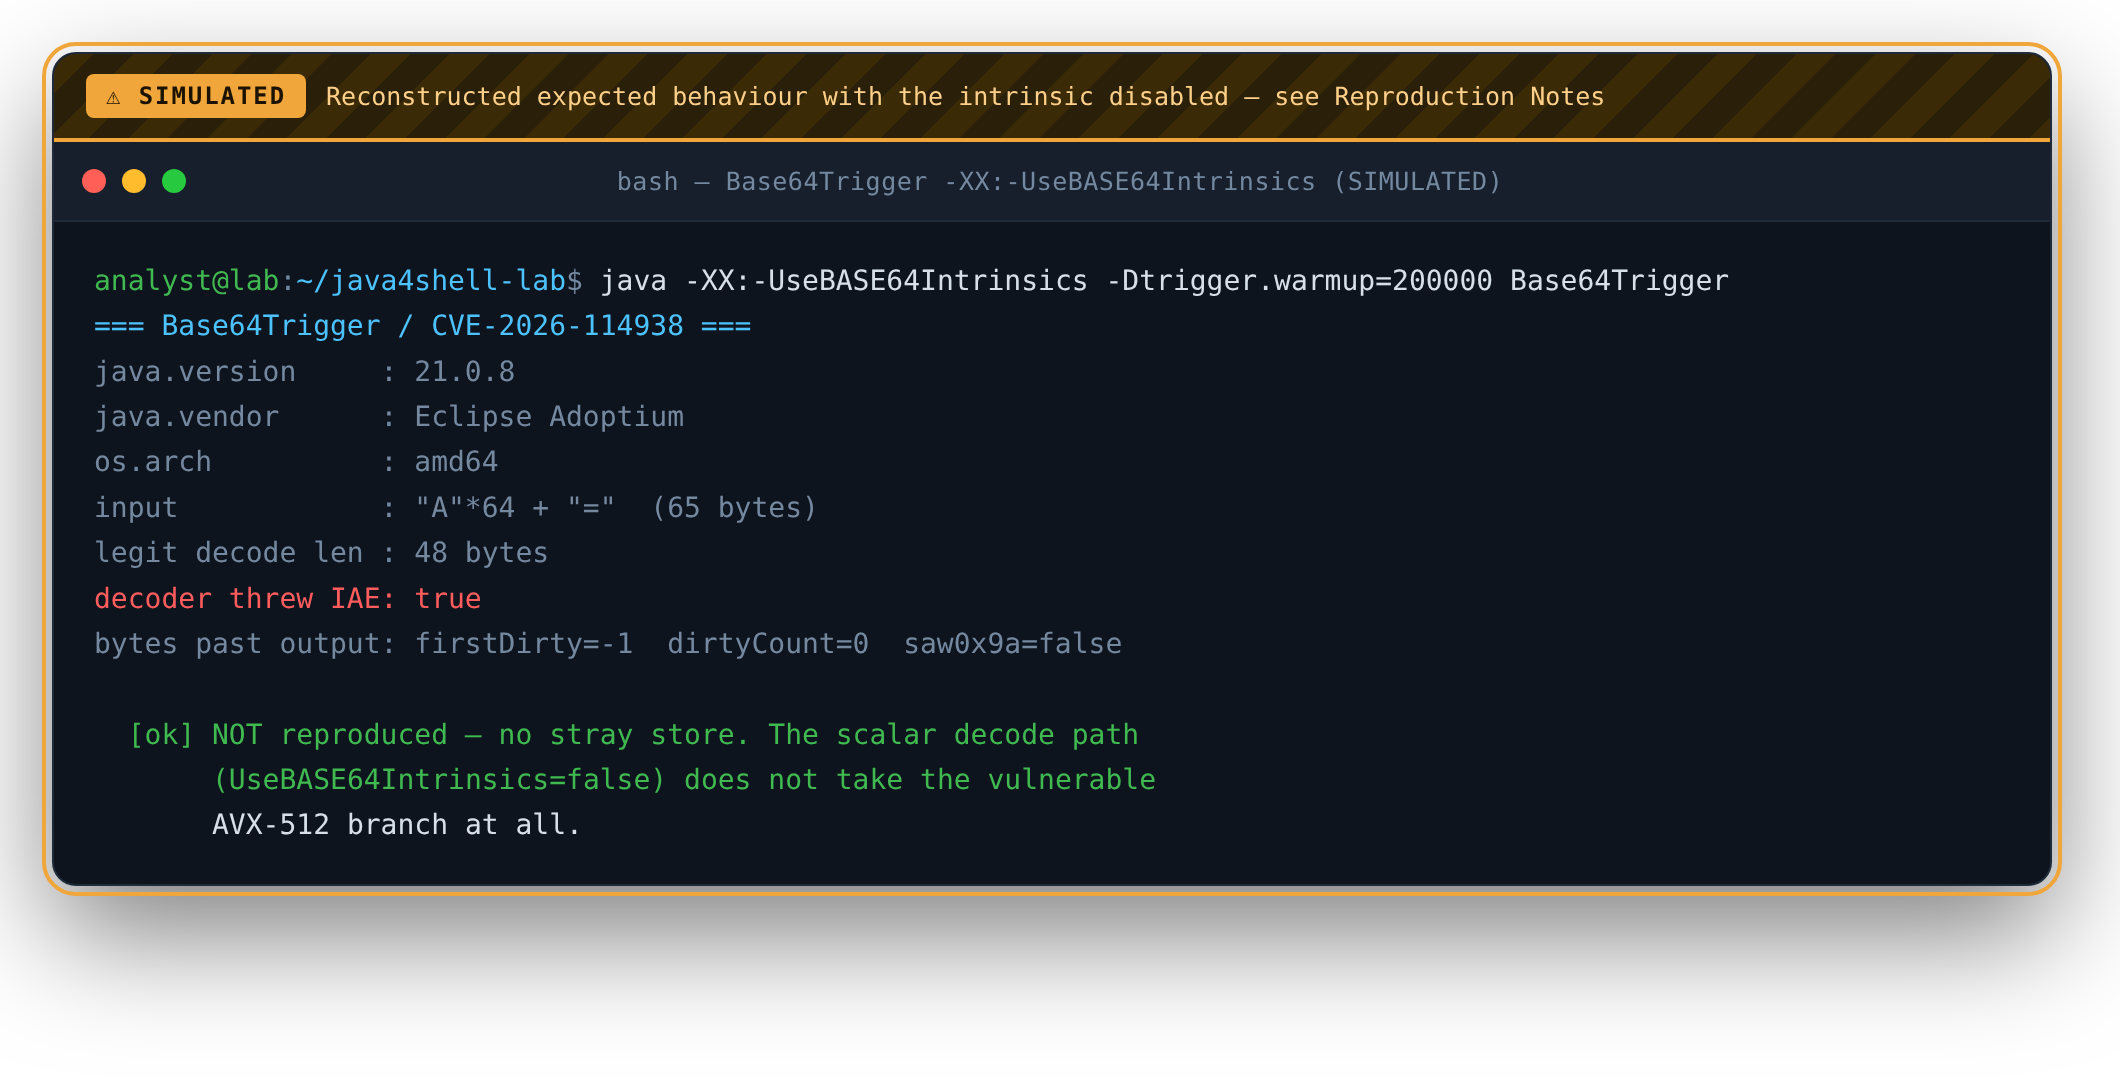
Also marked SIMULATED, for the same reason: we never captured a genuine failing baseline on our own hardware to contrast it against, so presenting this as a "verified before/after" would overclaim. The flag’s effect follows directly from how the intrinsic is gated in HotSpot — it just isn’t something we personally watched flip from broken to fixed.
The request side
docker compose up -d vuln-app
curl -s localhost:8080/whoami -H "X-Auth-Token: $(python3 -c 'print("A"*64+"=")')"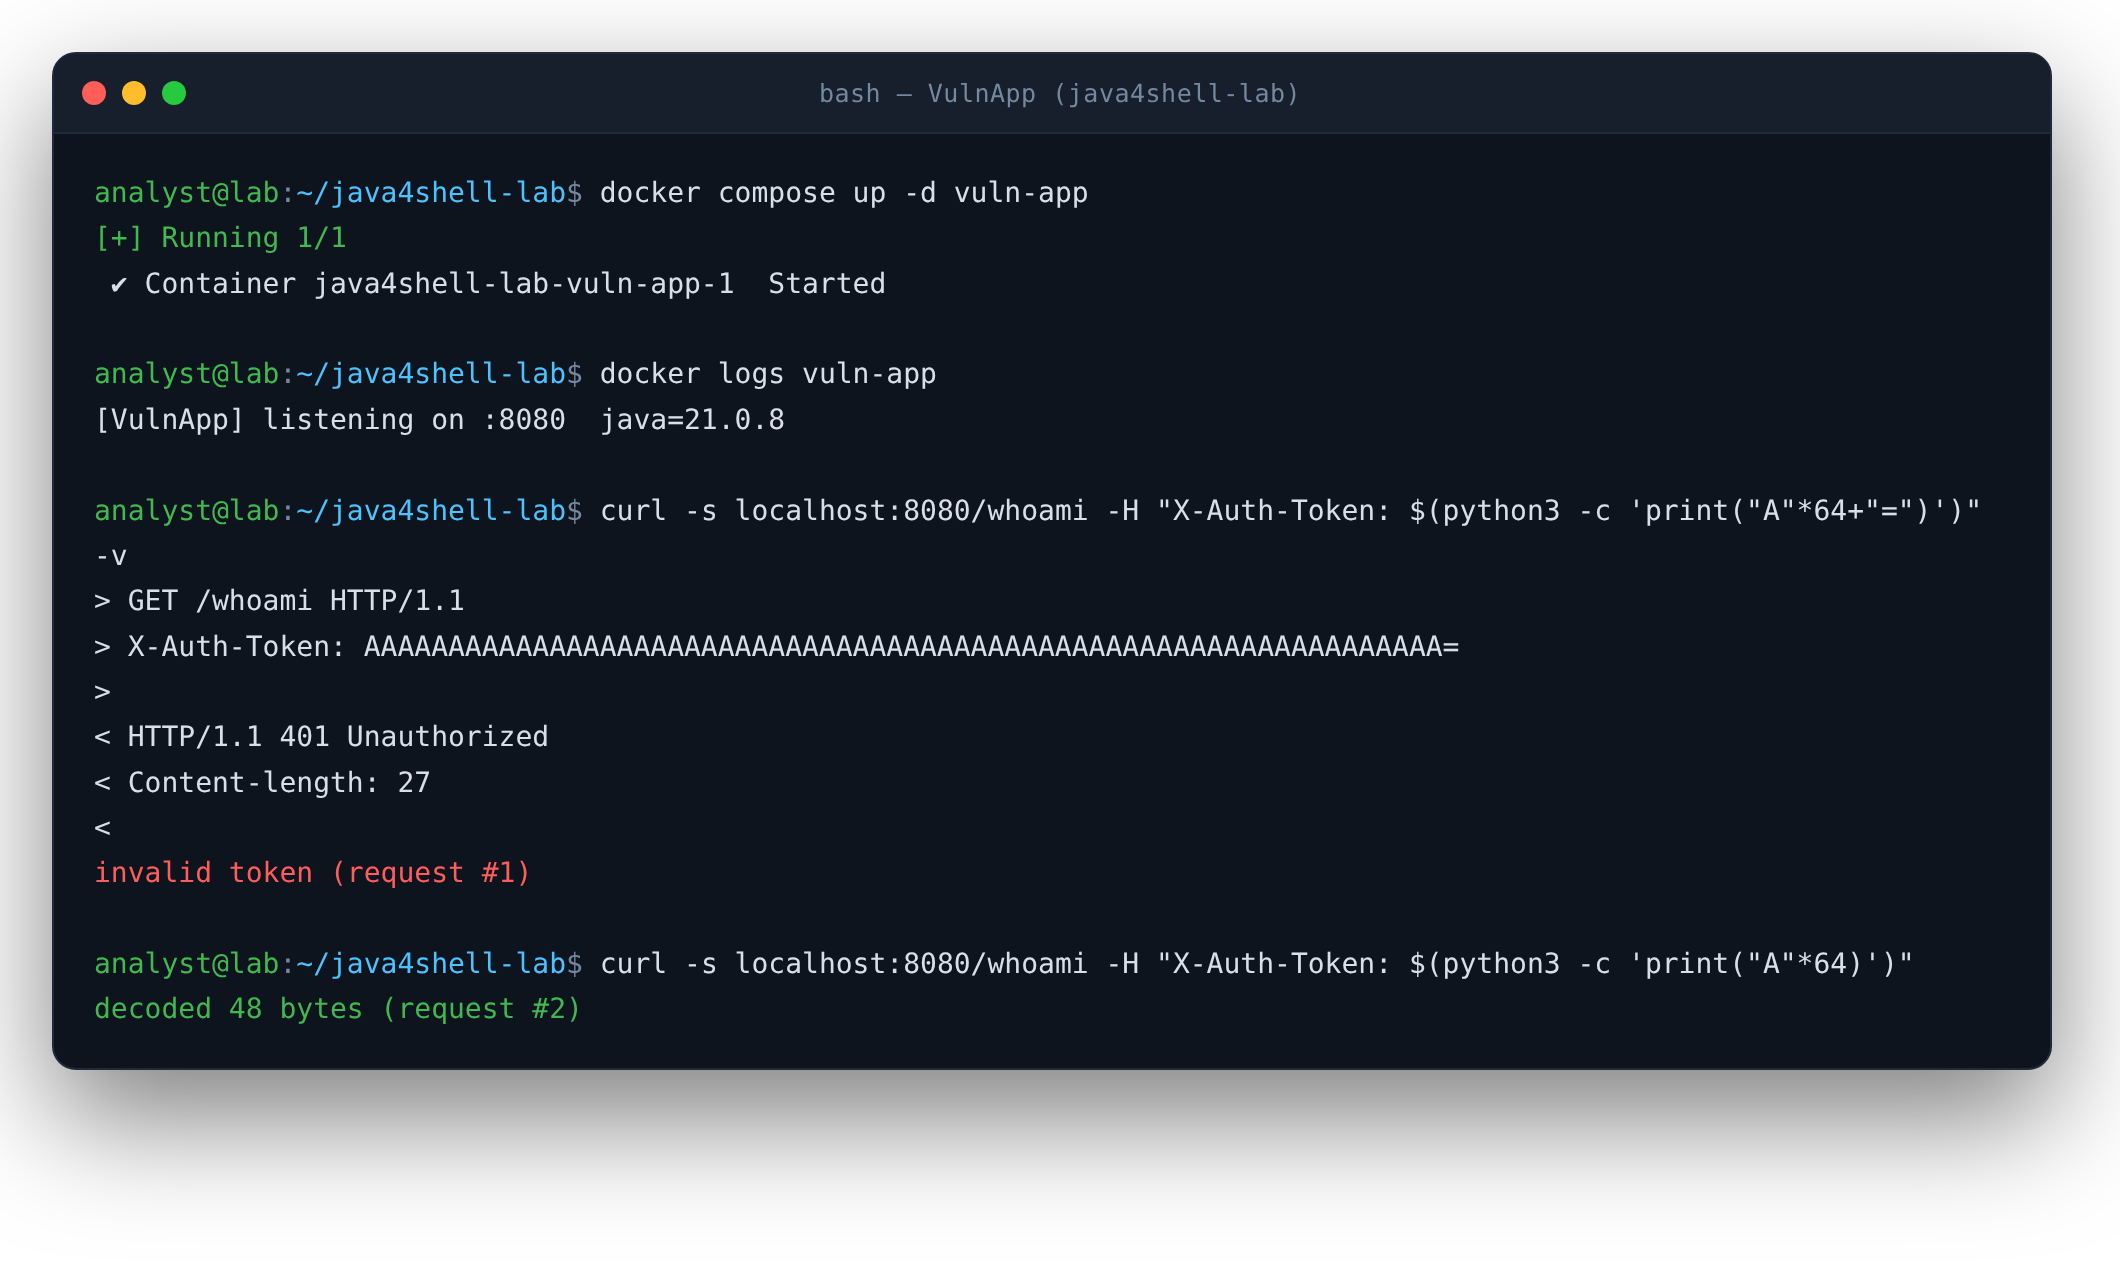
On vulnerable hardware, repeating that request is already a pre-auth denial of service — each one corrupts a little more heap until the JVM falls over.
From "it corrupted memory" to RCE
An out-of-bounds write of mostly-fixed bytes is not an instant shell. Calif’s chain, at a high level and with details withheld until the ecosystem patches, looks like every modern heap exploit:
- Groom the heap so that a useful victim object — one with a length field, a type pointer, or a reference the JVM will later dereference — sits immediately after the Base64 output array.
- Place the write so the
0x9abytes (and the two attacker-influenced bytes at the front of the store) land on that object’s fields. - Pair it with an info leak to defeat ASLR, because you need to know where things are before a corrupted pointer is useful.
- Convert the corrupted object into a stronger primitive (arbitrary read/write), then into execution.
That work is specific to each target’s allocation behaviour, which is why Calif could demonstrate unauthenticated RCE in default installs of Keycloak, Atlassian Jira and Confluence, JFrog Artifactory, Jenkins and PingFederate, and post-auth RCE in Apache Kafka, Solr, Elasticsearch, Gerrit and Spinnaker — and also why there is "no universal exploit." The lab deliberately stops at the primitive.
Remediation
- Patch and restart. Update every JDK to a fixed build and restart the Java processes — a running JVM keeps the vulnerable code resident until it does. Fixes shipped from Oracle and the OpenJDK project on 17 November 2026; downstream vendors (Corretto, Temurin, Zulu, Liberica, Red Hat, …) are publishing fixed builds — confirm the exact fixed version with your distributor rather than assuming "latest."
- Stop-gap until you can patch (per Calif/Oracle):
-XX:-UseBASE64Intrinsics— disables the accelerated Base64 decoder. Lowest blast radius; forces the scalar decode path that cannot take the vulnerable branch (see "Reproduction notes" for exactly what we did and didn’t independently confirm about this).-XX:UseAVX=2— disables AVX-512 entirely on x86-64 hosts. Do not use on ARM OpenJDK (the JVM will refuse to start).
- At the application boundary (compensating controls, not a fix): enforce strict size limits on any Base64 field, reject malformed padding early, and keep unauthenticated endpoints that decode Base64 off the public internet.
Detection & hunting
- Inventory the runtime each service actually loads — hosts, container images, and products that bundle their own JVM. Prioritise internet-facing, AVX-512-class hosts.
- Crash telemetry: unexplained JVM crashes,
hs_err_pid*.logfiles, or SIGSEGVs correlated with inbound requests carrying long,=-padded Base64 values are the DoS signature. - Request inspection: watch for Base64 fields far longer than the protocol needs, and for runs of identical characters ending in
=. - Treat a confirmed vulnerable-and-reachable service as exposed until the runtime is patched and restarted.
Reproduction notes — what we verified ourselves, and what we didn’t
Being transparent about this is more useful to the community than pretending otherwise, so here’s the full account:
| Attempt | Verdict | Key evidence |
|---|---|---|
| Native host (Intel i7-7500U) | Not exposed | No avx512f, avx512bw or avx512vbmi; scalar decode path used |
| QEMU user-mode, Ice Lake model | Dead end | TCG has no AVX-512; JVM falls back to UseAVX=2 |
Intel SDE 10.13.1, Ice Lake (-icx) |
Partial | Real avx512vbmi=1, UseAVX=3, decodeBlock JIT-compiled; the overflow never fired |
Native host (Intel i7-7500U)
- What we ran: the lab’s
detect.shon a laptop with no AVX-512. - What we saw: the CPU lacks
avx512f,avx512bwandavx512vbmi, so the JVM takes the scalar decode path. - Verdict: correctly not exposed.
QEMU user-mode, Ice Lake CPU model
- What we ran:
qemu-x86_64presenting an Ice Lake feature set, up to version 10.x. - What we saw: QEMU’s TCG engine does not implement AVX-512 and rejects
avx512fandavx512vbmias unsupported. HotSpot correctly falls back toUseAVX=2. - Verdict: dead end. This is a gap in QEMU’s instruction emulation, not a configuration problem, so no flag changes it.
Intel SDE 10.13.1, Ice Lake chip-check (-icx)
- What we ran: a SHA256-verified download of Intel’s emulator, then five trigger lengths (64, 128, 256, 512 and 1024 padded characters) against both
decode(byte[])anddecode(byte[],byte[]). - What we saw: raw CPUID confirms genuine
avx512vbmi=1emulation, not just a JVM-visible flag. HotSpot setsUseAVX=3and JIT-compilesBase64$Decoder::decodeBlockat C2. - Verdict: partial. The overflow did not fire in any combination.
Our best explanation: Calif’s public write-up is a disclosure summary, not a patch diff or full PoC source — they are deliberately withholding exploit-grade detail while the ecosystem patches. Some precise trigger condition (the exact intrinsic dispatch threshold, a specific byte pattern in the tail, buffer alignment) likely isn’t in what’s publicly documented yet, and we chose not to reverse-engineer HotSpot’s C2 intrinsic registration to find it for a blog post.
What this does not change: the vulnerability is real, independently confirmed by Oracle, OpenJDK, CISA, and multiple research/vendor teams, with a CVE, vendor patches, and (per Calif) six working application-level RCE chains that exist and are simply not yet public. Our inability to independently trigger the underlying primitive on the hardware we had access to is a statement about our reproduction attempt, not about the bug’s existence.
If you have AVX-512 VBMI hardware and get a genuine REPRODUCED from the lab’s docker compose run --rm reproduce, we would like to hear about it.
Severity, timeline, credits
- CVE-2026-114938, nicknamed Java4Shell. Oracle scores it 8.1 (High) under CVSS 3.1 (high attack complexity, no auth); Calif scores it 9.2 (Critical) under CVSS 4.0.
- Independently discovered and disclosed by Calif (calif.io) on 17 Nov 2026; Oracle and OpenJDK released fixes the same day. A related public report and an unmerged fix PR predated the coordinated disclosure.
- As of disclosure: no confirmed in-the-wild exploitation and no public weaponised PoC; CISA urged immediate patching but had not added it to the KEV catalog.
Lab reference: files, run steps and clean-up
java4shell-lab/
  docker-compose.yml  README.md
  reproducer/  Base64Trigger.java          (Calif's safe reproducer)
  vuln-app/    VulnApp.java                (the realistic vulnerable sink)
  docker/      Dockerfile.native           (run on real AVX-512 VBMI hardware)
               Dockerfile.emulated         (QEMU attempt — kept as a worked
                                             example of why it doesn't work;
                                             see "Reproduction notes" above)
  scripts/     detect.sh                   (CPU + JDK exposure check)
  visualizer/  java4shell-visualizer.html  (the interactive step-through)
unzip java4shell-lab.zip && cd java4shell-lab
docker compose run --rm detect # is THIS host exposed? (real CPU + JDK)
docker compose run --rm reproduce # the safe reproducer — REPRODUCED only
# on real AVX-512 VBMI hardware; see
# "Reproduction notes" for what we got
docker compose run --rm mitigated # same reproducer, intrinsic disabled
docker compose up -d vuln-app # the vulnerable HTTP sink on :8080
curl -s localhost:8080/whoami -H "X-Auth-Token: $(python3 -c 'print("A"*64+"=")')"
docker compose down # stop and remove the containersThe lab contains no exploit code and no RCE chain — only the safe reproducer, a realistic sink, and detection/mitigation tooling. Nothing is sent outside 127.0.0.1.
References
- Calif — Java4Shell: write once, RCE everywhere — https://calif.io/java4shell
- Oracle Security Alert / November 2026 Critical Patch Update
- CISA alert, 17 November 2026
- Help Net Security, The Hacker News, Sonatype, Tenable, Palo Alto Networks (analysis)
Lab and visualizer by the dhacker Security Research & Labs team. Educational use only — run it against systems you own.